Main section
What Certificate Transparency Logs reveal about your organisation
In our previous post, we explored the role of Certificate Transparency (CT) Logs and why SwissSign is setting up its own log. CT exists to keep browsers honest. But the same public record that protects web users also gives enterprises something most security teams don't have today: a continuous, independent audit trail of every publicly trusted certificate tied to their domains.
From CT logs to monitoring services
A CT Log records a certificate the moment any publicly trusted CA issues one for your domain, not just the certificates your organisation requested through its own procurement. That includes certificates issued for subsidiaries, marketing microsites, SaaS and CDN platforms provisioning on your behalf, agencies and suppliers managing web properties for you, and forgotten development or staging environments. If it's publicly trusted, it ends up in the log, whether IT knew about it or not.
CAs can submit a certificate to logs from any of the roughly 11 log operators currently accepted by browsers — around 16 logs in total, mostly temporal shards, with each operator running about two per year — and there's no requirement to stick to the same ones each time. Watching a single log, or even a handful, isn't enough to catch everything issued for your domains — full visibility means monitoring all qualified logs at once.
That's where CT Log Monitors bring their value: a monitor fetches certificates from every log and gives domain owners a way to search for their own domains specifically. Well-known monitors like crt.sh or Censys are usable with limited availability or on a free tier; a list of recognized monitors is maintained at certificate.transparency.dev/monitors.
Discover certificates beyond your internal inventory
CT logs answer a question internal inventory often can't: what public certificates actually exist for our domains and subdomains right now, regardless of who issued them or requested them.
Internal records go stale fast. CT visibility tends to fill gaps like:
-
Certificates belonging to recently acquired subsidiaries or business units not yet folded into central IT.
-
Certificates issued by suppliers, MSPs, or agencies managing a web property on the company's behalf.
-
Certificates auto-issued by SaaS platforms and CDNs that IT never provisioned directly.
It doesn't stop at an exact inventory, either. That same visibility gives insight into what kind of certificates are actually used: validation type, certificate category (single domain, multi-domain SAN, wildcard), crypto algorithm in use, validity and expiration trends, and an exhaustive list of the endpoints referenced across your certificates.
None of this replaces an internal CMDB or certificate inventory. It's a way to check one against reality, independent of whether anyone remembered to record an issuance.
What your certificate landscape reveals about hidden risks
Once you can see the landscape, a handful of patterns tend to surface again and again:
-
Weak or non-compliant issuance. Free, automated CAs are a fine choice for low-risk services, but they offer no organizational identity check. Where verified organisational identity is required, OV or EV certificates are a more suitable choice. Wildcard certificates and oversized SAN lists compound the risk: every subdomain or hostname they cover shares the same point of failure.
-
Decentralized or shadow issuance. Certificates from CAs outside your approved list, or OV/EV certificates validated under several different legal entities, are usually a sign that a team or subsidiary went around the governed process — untracked in inventory, untracked in the audit trail. The same hostname covered by certificates from more than one CA is a related signal: two systems issued independently, without coordinating.
-
Grouped renewal periods. When a large share of certificates expires in the same window, renewal workload spikes sharply, and so does the chance of a missed or rushed one. As certificate lifetimes shorten, a clear overview of expiry dates becomes even more important for identifying renewal peaks early.
-
CA jurisdiction. For government, financial, and critical-infrastructure domains especially, it's worth knowing which legal system governs your certificates and where the issuing CA is headquartered — increasingly a question regulators and auditors ask directly, not just an infrastructure detail.
-
Exposed naming patterns. The same visibility that helps you find shadow IT also means anyone else can see your domain naming patterns: a subdomain like internal-crm.company.com becomes publicly visible the moment a certificate is issued for it, even if it was never in public DNS.
Get your certificate landscape report
Discovery and risk identification come together in one deliverable: a personalised certificate landscape report for your domain. It is a live snapshot of every publicly trusted TLS/SSL certificate issued for your domains (issuer, validation level, key algorithm, certificate type, and expiration timeline), alongside the endpoints actually running them, since discovery routinely turns up more live hosts than certificates on record. Each risk pattern above is flagged directly in the report, with a concrete recommendation attached.
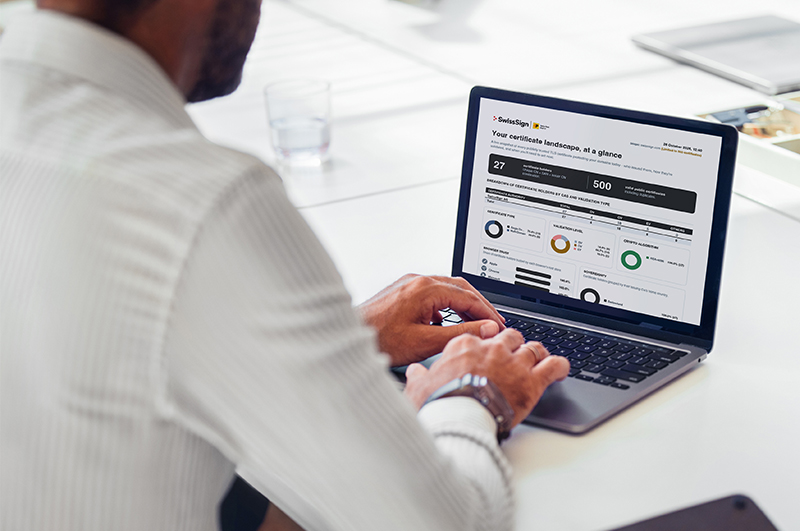
There are many good reasons to start with a report:
-
Get visibility of your public certificates, including the ones nobody told IT about.
-
Prepare for shorter certificate lifetimes and the automation they require.
-
Switch or consolidate certificate authorities.
-
Plan post-quantum readiness and crypto-agility, starting from the algorithms and key sizes actually in use.
-
Support audit and compliance work (ISO 27001, PCI DSS, NIS2, and sector-specific frameworks like DORA or FINMA's operational resilience requirements for financial services).
-
Get a fast read on an acquisition target's certificate footprint, or give leadership an actual number to report instead of an estimate.
From a one-off report to continuous certificate monitoring
A report is a snapshot. The best value comes from continuous, automated monitoring, especially for critical services: near-real-time alerts whenever a new certificate is issued for one of your domains, rather than finding out weeks later.
CT monitoring isn't about tracking when your own well-known certificates are due to expire — that's already handled by your CLM platform or by the issuing CA itself. The real value shows up elsewhere: catching what happens to your domains outside your own issuance process. For medium to large enterprises — organisations with complex, distributed teams, well-known brands, or critical public-facing services — that means detecting misuse before it turns into a governance problem, a shadow IT surprise, or a phishing attempt aimed at your own users. Continuous monitoring can catch a certificate issued by a CA outside your approved list, one issued under a non-compliant algorithm policy, or an organisation-validated certificate suddenly issued to a new or third-party entity for one of your domains.
Coupled to a CLM, it goes further still: instead of a bare alert, each newly discovered certificate lands directly in your governed inventory, scored against your policy, and ready to be assigned an owner and tracked like everything else you manage. Not everything that surfaces this way needs to be brought under central control. Plenty of it is legitimately managed by a subsidiary, a supplier, or a SaaS platform, and that's fine. What matters is that each one is tracked and has an identified business owner, so if something changes — an unexpected renewal, an unfamiliar issuer, a domain nobody claims — there's someone to ask.
This is where SwissSign helps: our Certificate Lifecycle Management platform handles governance and automation for the certificates you already manage, and the certificate landscape report is a first step toward bringing the rest under the same roof.